Enhanced Conversions
Feed Google the conversions its pixel missed
Hashed customer identifiers travel alongside the purchase event, recovering the conversions a cookie-only match drops.
How it works
TrustData is the conversion hub. It captures events from your backend and forwards them to each platform's server-side API, so nothing depends on what the browser allows.
Hashed customer identifiers travel alongside the purchase event, recovering the conversions a cookie-only match drops.
Purchase, lead and custom events go server to server with a deduplication key attached, so the sale counts once.
Server-side forwarding supplements or replaces the pixel on the channel most affected by blocking.
sGTM integration
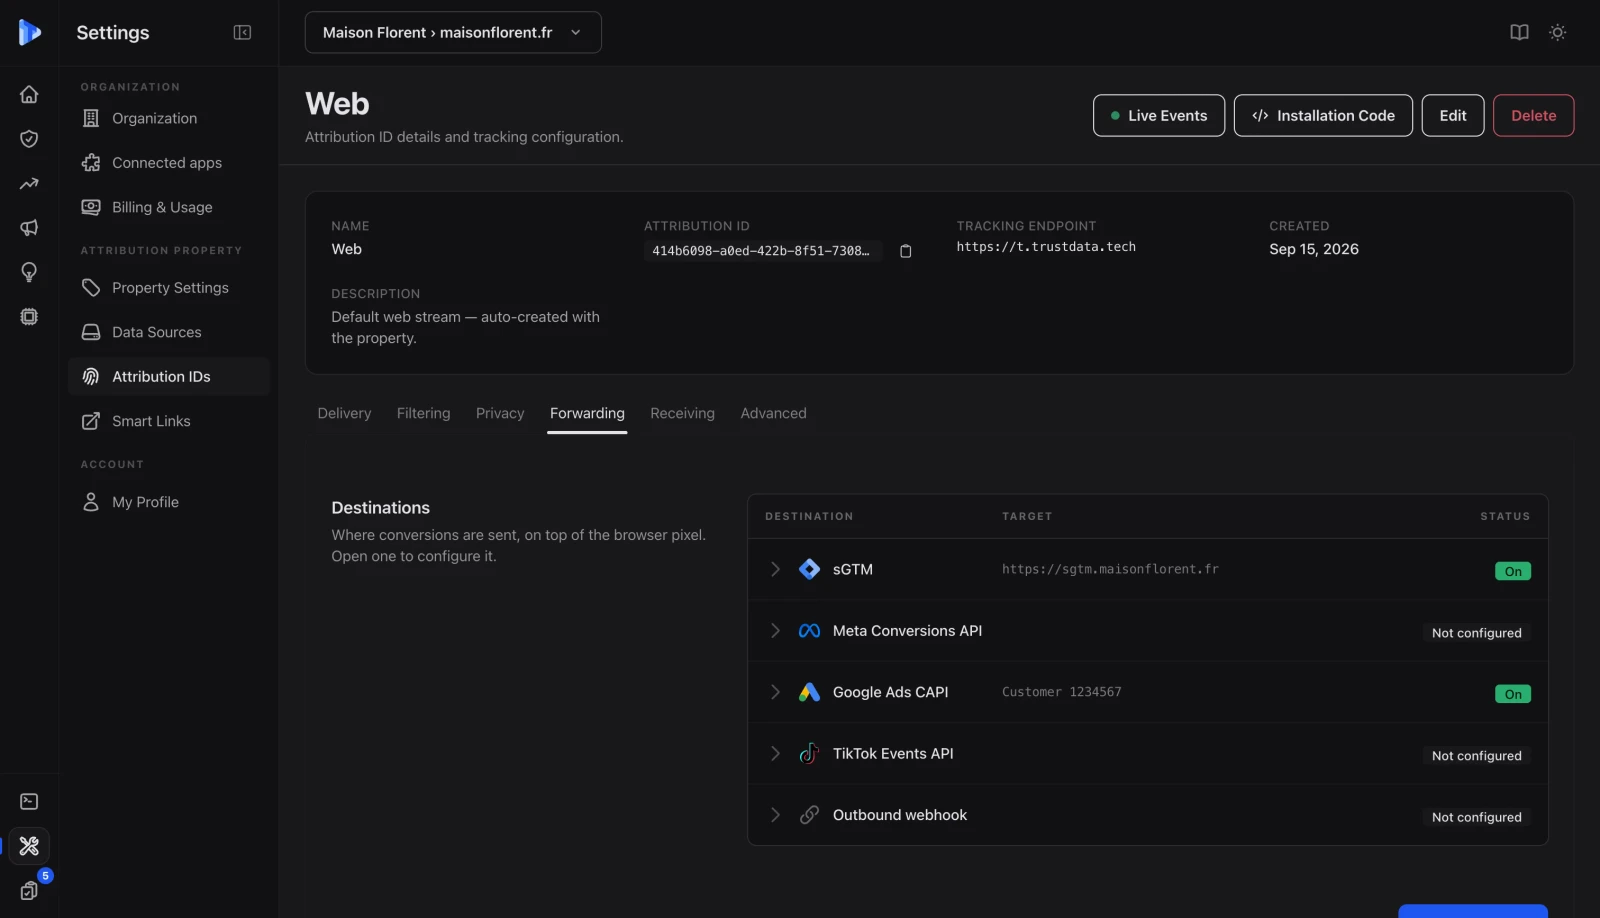
If you have an existing sGTM container, TrustData can forward enriched conversion events to it instead of (or alongside) forwarding directly to platforms. You keep full control over your tag logic.
Conversion events arrive as HTTP requests to your server-side GTM endpoint, and your existing tags fire on them unchanged.
Order value, product data and customer identifiers are appended before the event reaches your container.
Your sGTM container stays in charge of what leaves for Google, Meta and TikTok. TrustData is the data pipe.
Setup
Configure your conversion events once in TrustData. We handle the mapping and formatting for each platform's API automatically.
Purchase, lead or signup is translated into each platform's own shape without you writing the mapping.
Events forward within seconds of capture, with no nightly batch between the sale and the platform seeing it.
What consent changes
A visitor who blocks the pixel has usually also declined advertising cookies. The sale still counts in your reporting. We do not forward it, and the gap between the two numbers is a real constraint rather than something to paper over.
Every conversion the SDK records, including those where the platform pixel was blocked. This is what your true ROAS is built from.
Only conversions from buyers who accepted advertising cookies, checked before the event is built.
Consent, and nothing else. The gap between them is a real constraint on what any tool can do.
FAQ
Instead of relying on browser-based pixels (Google Tag, Meta Pixel) to fire on conversion pages, TrustData captures the event server-side, from your Shopify webhook or backend, and forwards it directly to each platform's server API. This bypasses ad blockers and ITP entirely.
Your container forwards what the browser handed it, so a blocked pixel is a conversion sGTM never receives. TrustData captures the event from your backend, enriches it with order value and customer identifiers, then posts it to your existing sGTM endpoint, where your tags fire on it unchanged. You keep the container and the tag logic, and the events arrive that were not arriving before.
Ad platforms handle deduplication on their end when they receive both a browser pixel and a server-side event for the same conversion. Check each platform's deduplication documentation for how to configure this in your existing pixel setup.
Yes. PII (hashed email, phone) is only forwarded to ad platforms for users who have given explicit marketing consent. Anonymous server-side events (without PII) can be sent without consent for aggregate counting.
Currently Google Ads (Enhanced Conversions), Meta Ads (CAPI), TikTok Ads (Events API), and server-side GTM. LinkedIn and Pinterest are on the roadmap.
14-day free trial
14-day free trial. Server-side forwarding set up in under 30 minutes.